Most infrastructure platforms ask you to choose. A developer portal catalogues what you already run but cannot build any of it. A hosting platform builds quickly but only on its own cloud, with its own opinions. Wayfinder does the building, in your cloud accounts, against the modules and charts your platform team already maintains.
There are four things it does, and the site is organised around them.
Onboard a team
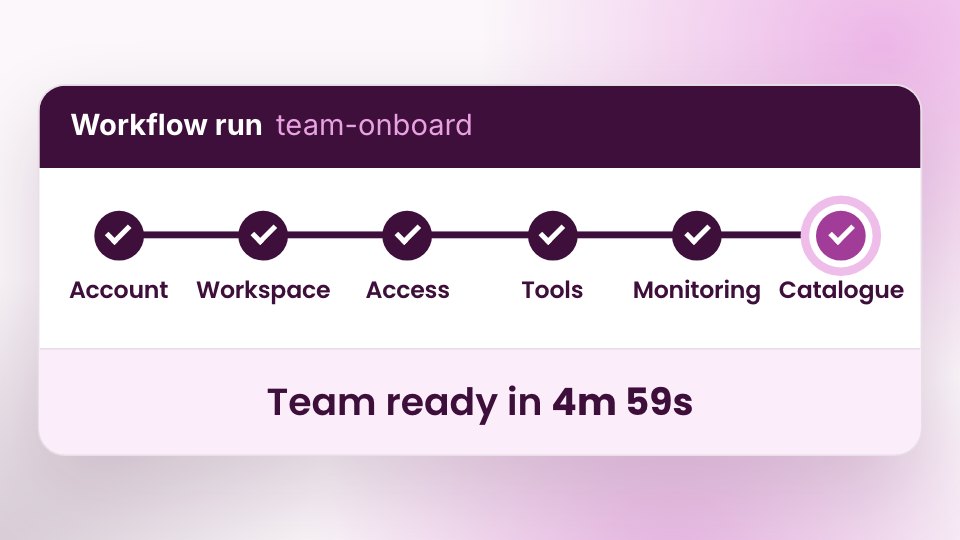
Getting a team ready to build usually means tickets to several other teams: one for a cloud account, one for access, one for repositories, one for monitoring. A Wayfinder workflow does all of it in one run. A workflow is a trigger and a set of tasks, and a task can call a web API, run an agent, check out a repository or run any CLI command. wf invoke team-onboard creates the account, scopes the access from your identity provider, connects the team's tools and stands up their dashboards, and the run is recorded so the next team is set up the same way.
Ship to any cloud
A developer describes an application in one file. wayfinder.yaml lists the components: a container to run, a database, a queue, a bucket. wf up deploys it to AWS, Azure, Google Cloud or Kubernetes with identity, policy and networking already configured, and wf down removes it in dependency order when the pull request closes.
What a developer can choose comes from the catalogue, and the catalogue is yours. Any Terraform or OpenTofu module becomes a cloud resource plan; any Helm chart becomes a Kubernetes resource plan. An agent drafts the plan from the module, deploys it for real to prove it works, and you fix the values that matter before publishing it. A repo template does the same for new services, so CI, scanning and identity are configured before the first commit.
Operate with agents
This is the part that changed most. An agent in Wayfinder is not a fixed feature: it is a prompt, the tools it may call, the shape of the answer it returns and the identity it runs as. Some ship with the platform, including the Assistant that answers questions about your own infrastructure and the agents that author and test plans. The rest you write. Agents also read skills: written knowledge, with files and tools of its own, that you author once and point the right agents at, so they follow how your organisation actually works rather than a prompt somebody keeps editing.
Put an agent behind a workflow and it does operational work on its own. An alert arrives from your monitoring tool, an agent investigates using the tools you gave it, tests the fix in a replica environment and opens a pull request with the results. A cost signal from any of the three clouds arrives the same way. A new module version is surveyed against every service using that plan, tested, and raised as one pull request per repository.
Those agents reach your other tools through integrations. An integration packages what a tool sends you as a webhook, what you call on it as a web API, and its MCP server, all behind one credential. Anything with a webhook, an API or an MCP server can become one, and your teams can write their own.
Govern the whole thing
Self-service without limits is how platforms get retired. In Wayfinder the limit is a setting, per team and per agent. You choose whether a team can publish its own plans, claim repositories, write its own workflows, add its own integrations or define its own agents, and you change it as they earn it.
Agents sit under the same rules as people. Each one runs as its own service account with the roles you grant it, and can never be granted more than the person who wrote it holds. Agents with a shell run in a sandbox on a node created for that run. Approval gates sit on whatever changes you choose. Every action, and every agent conversation, is recorded and can be replayed, so an audit is a query rather than a project.
Who it is for
Platform teams who are the bottleneck and want to stop being one without losing control. Developers who want an environment now rather than after a ticket. Security and engineering leadership who need to say exactly what each team, and each agent, is allowed to do.
The free tier runs a real application in production, in your own cloud account, with every feature. Start free, or book a demo and we will walk through it against your own setup.